- 09:02 User authenticated.
- 09:31 Someone else is at the keyboard.
Catch hijacked sessions while they happen
Most security tools assume that after a token is assigned, the user is the same person throughout the authenticated session. This fallacy is exacerbated by longer, legitimate AI-engaged sessions.
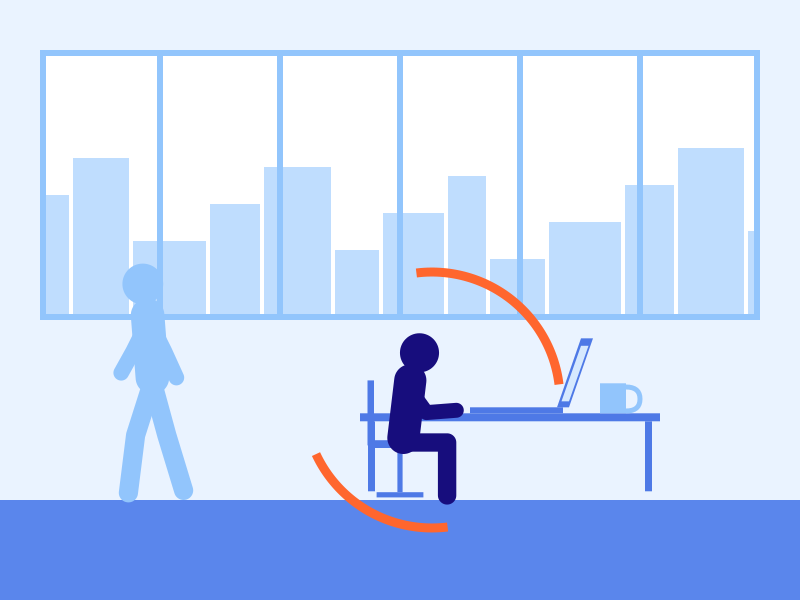
The token was valid.
Who is using it is not.
A credential is not a person. Once a session is authenticated, it is trusted until logout. A stolen session token skips authentication altogether, and someone with a stolen or shared password looks exactly like the owner.
Mimoto continuously verifies it is always the correct person, machine, or agent.
39%
of breaches involved credential abuse at some point in the attack, still the most common factor.
What a takeover looks like to Mimoto
One session, from authentication to logout
At authentication
Authentication confirms the credential once, at the door.
During the session
Most tools stop checking here. Mimoto keeps checking that it is a real human and the right human.
All session long
The same checks recognize an AI agent posing as the person, and Mimoto responds in real time.
Frequently asked questions
Doesn’t Zero Trust protect against hijacked sessions?
Zero Trust verifies the artifacts of identity (tokens, tickets, assertions, device posture) rather than the person. Mimoto works with Zero Trust to add continuous verification of the person.
Is it possible to hijack an active session?
Hijacking an active session has become increasingly easy. In addition to breaches that have gained access from reverse shells or compromised credentials, live in-person takeovers are aided by an increase in unmonitored session length that often accompanies workers’ use of agentic AI. Have you ever stepped away to get a cup of coffee while your agent completes a task? Yep. Thought so.
See where the gap sits in your environment
Want to see Mimoto catch the wrong person in a live session? We will set up a time.