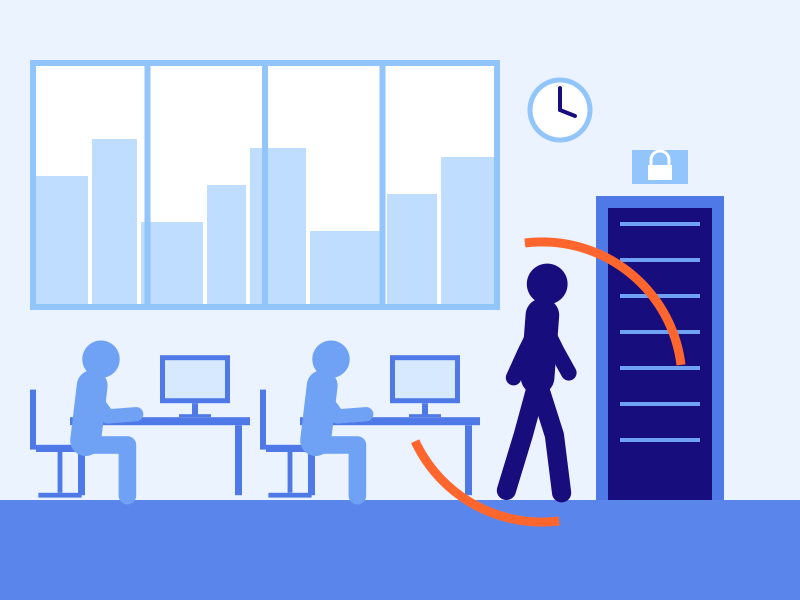
- 08:47 Worker authenticates credential.
- 14:12 Same user uses a shared credential to access sensitive data without authority.
Catch insider threats while they happen
An internal bad actor accessing sensitive data may have used another employee’s credentials or a shared account. It may be internal access from someone who shouldn’t have it, or malicious activity disguised as normal work. That is what makes insider threats “unseeable.” Mimoto reacts to insider threats as they are happening, not in next quarter’s audit.
Insiders already passed every check
The hardest threat to see is the one already in your protected perimeter.
$17.4M
average annual cost of insider risk for an organization. Incidents took 81 days to contain on average.
Source: Ponemon Institute, 2025 Cost of Insider Risks Global Report
How Mimoto catches it
Mimoto combines advanced pattern matching with anomaly detection to recognize each specific person and respond to malicious activity.
Analyze
Measures how each person interacts, never what they type.
Verify
Confirms the person in the session matches the person who owns the account.
Enforce
Responds to a mismatch in real time: alerts your team, and re-verifies, restricts, or ends the session, your policy enforced automatically.
What changes for your team
Before Mimoto
- Insider activity often surfaces in an audit or an investigation, after the damage.
- Logs show the account, not the person behind it.
- Every action looks legitimate, because the authentication was.
With Mimoto
- A response in the session, while it is happening.
- The person checked, not just the account.
- A proportional response, from a quick re-verify to ending the session.
Verification, not surveillance
Employees are the foundation of any successful organization. Balancing insider threat security with protecting employee privacy is a cornerstone of Mimoto Continuous Verification.
Mimoto measures how a person interacts, never what they type or what is on the screen.
Frequently asked questions
How does Mimoto protect user privacy while securing systems and data?
Mimoto never captures raw keystrokes or PII. We don’t follow credentials around and don’t monitor employee output. It’s a matter of privacy, of global regulatory compliance, of not becoming a vector ourselves, and of what we believe is just the right thing to do.
Can shared accounts, such as admin accounts, be secured with Mimoto?
Yes. Because Mimoto utilizes person-specific profiles, it is able to consider multiple people assigned to a shared account, or assigned to use a shared device during a specific shift.
See where the gap sits in your environment
Want to see Mimoto catch the wrong person in a live session? We will set up a time.